Snowflake Cortex AI Gateway
Extend Snowflake’s control plane to every agent so you can monitor actions, govern connections and optimize AI spend.
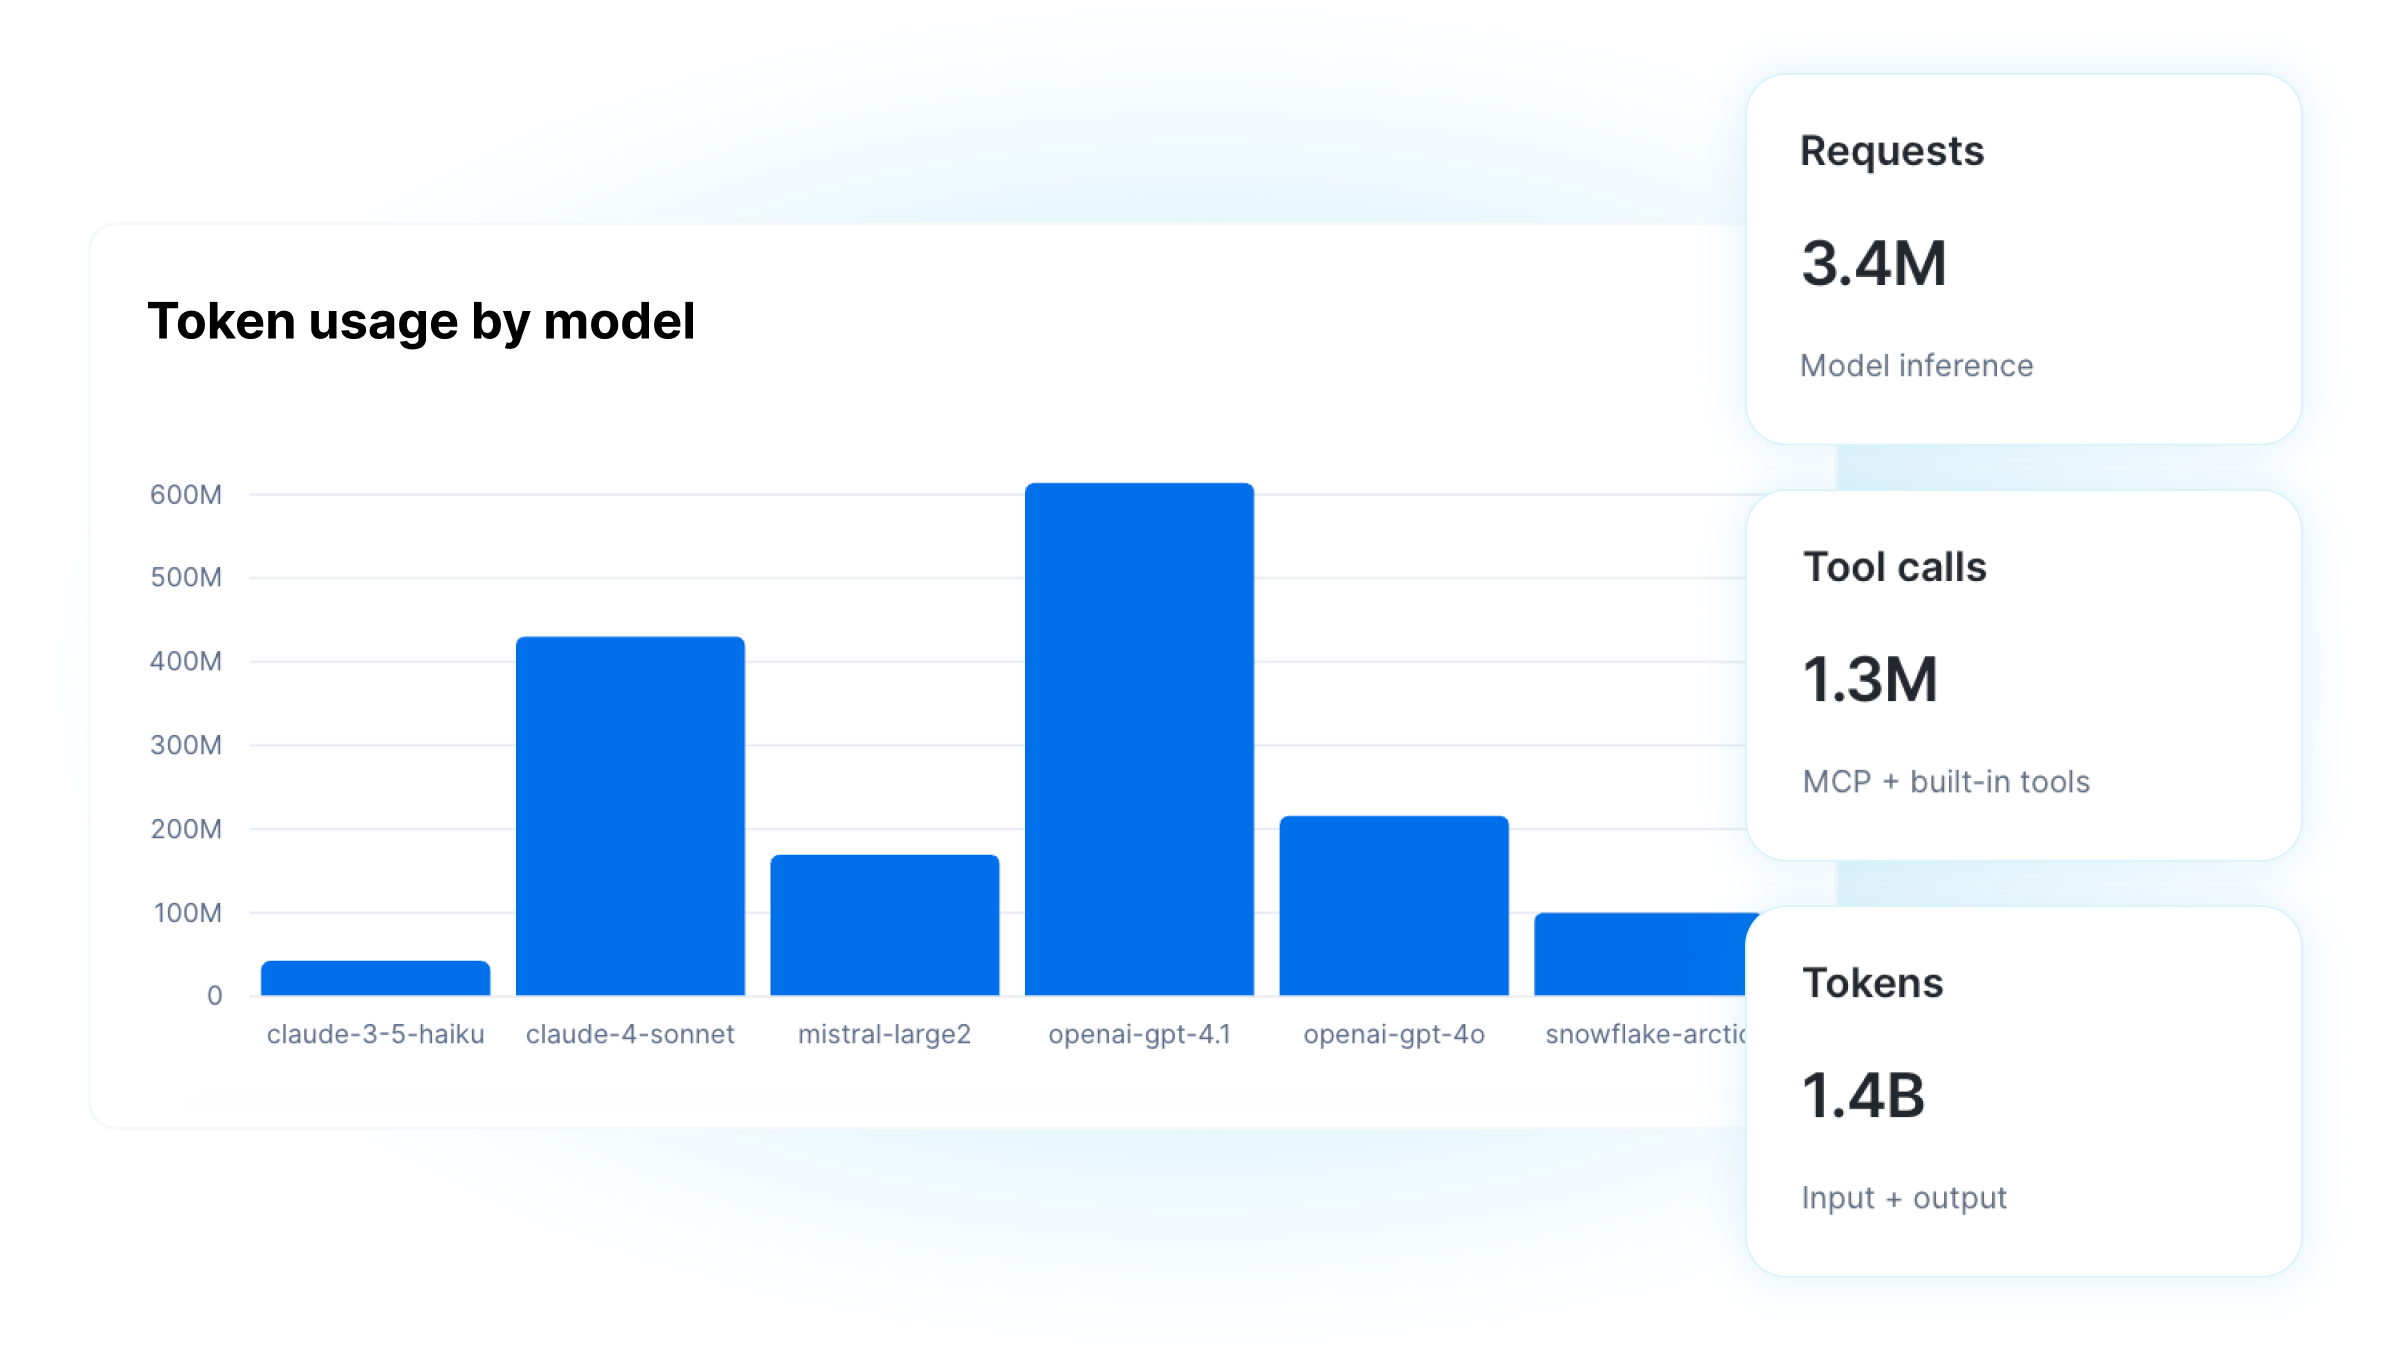

Get full visibility into agent telemetry
See which tool or model was called, in what order and by whom — alongside your business data.

Prevent unsanctioned agent access
Enforce approved actions across 100+ MCP servers using the identity policies you already have in Snowflake.

Optimize AI ROI
Control costs and match each task to the model that delivers the most value.
Benefits
Deploy trusted agents across clouds, models, frameworks and tools
Agent observability
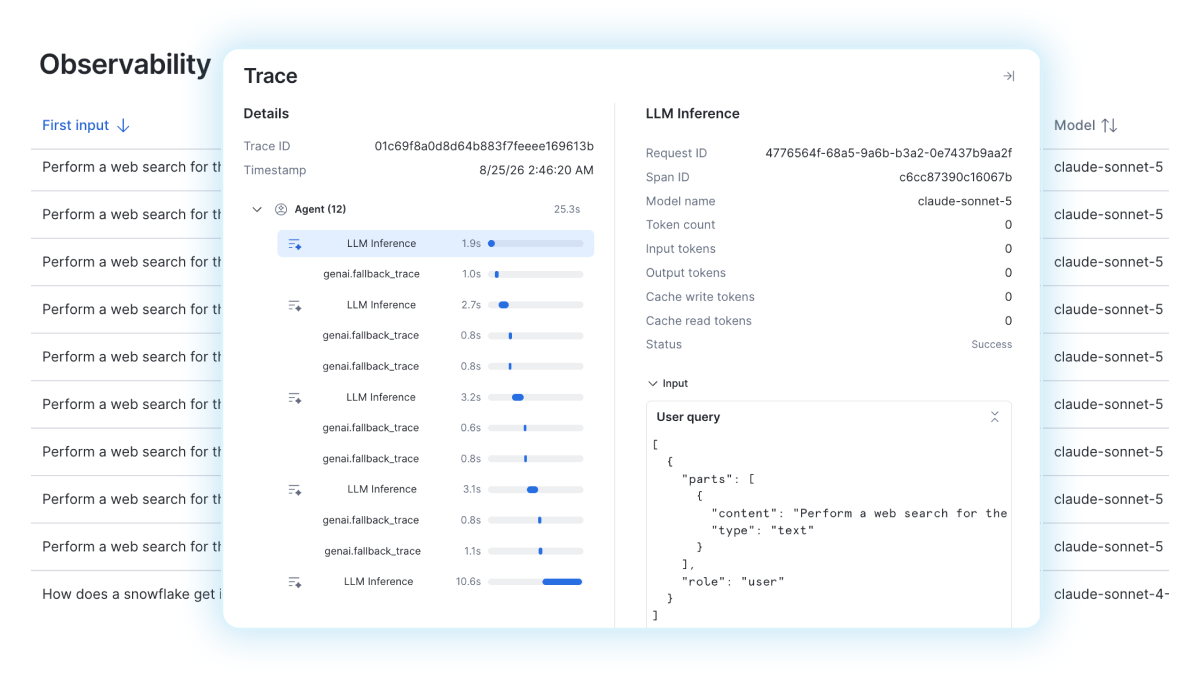
Observe agent behavior alongside business context
- Correlate action actions with business data to measure their impact.
- Query agent actions with SQL or Snowflake CoCo to assess operations and risk.
- Correlate agent behavior with business data to measure impact.
Agent access governance
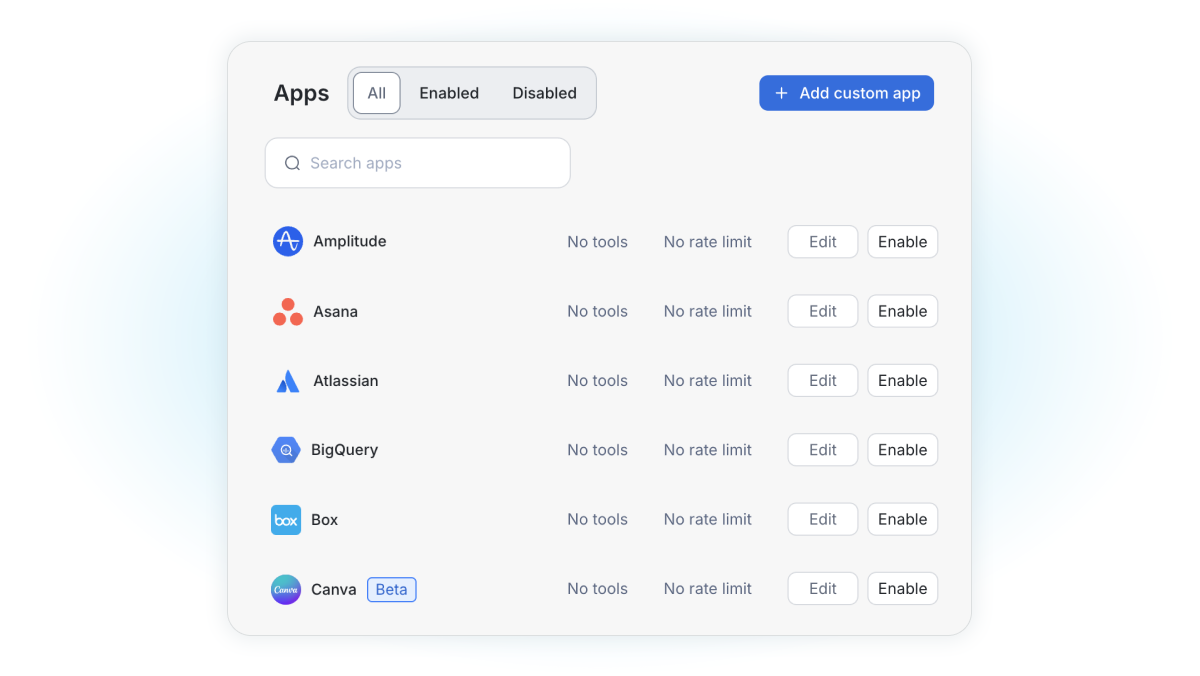
Control how agents access tools and models†
Block unauthorized Model Context Protocol (MCP) tool calls before execution to prevent incidents with Cortex AI Gateway Tools.
Scale governance with Snowflake role-based access control (RBAC) as deployments grow.
Govern from where the data lives — no exports, no new platform, no separate access request.
Give agents access to approved tools without hardcoded credentials, so an agent does not exceed its current authorization.*
AI economics
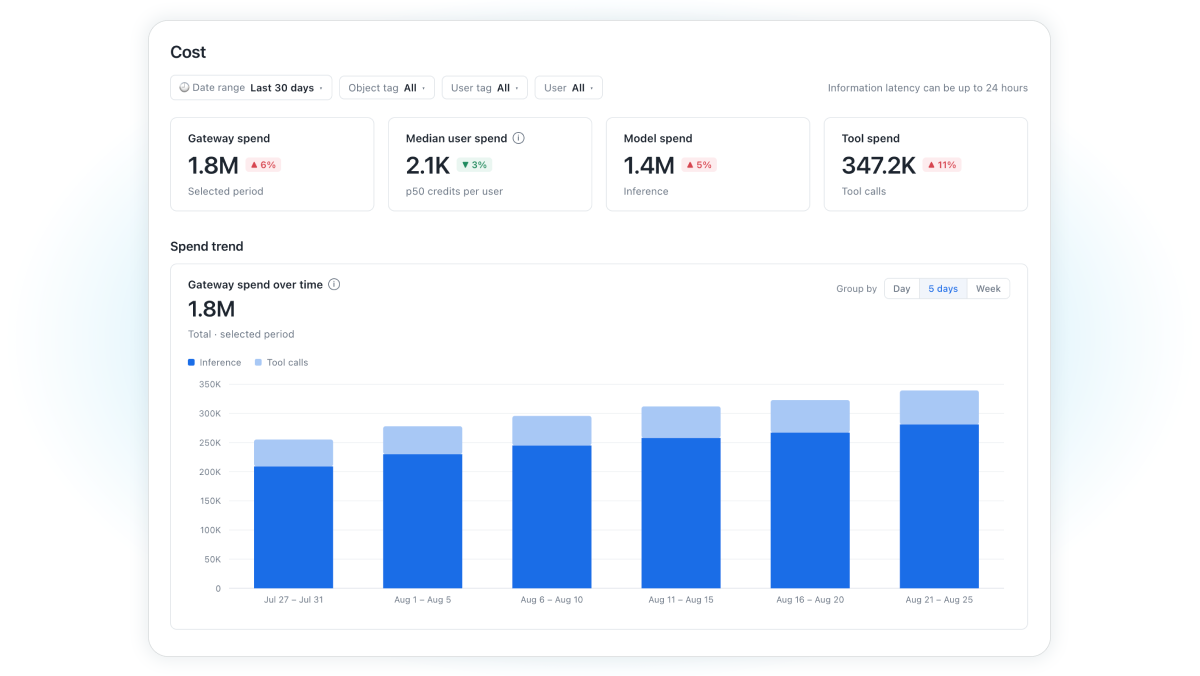
Rightsize spend across AI workloads†
Attribute AI costs by team, agent, department or app to measure ROI.
Set spend limits that stop runaway agents before they breach your approved budget.
Use data from every agent interaction to improve AI economics over time.
Route requests automatically by cost, accuracy, latency and customer preference.*
Access a growing portfolio of open and proprietary models within Snowflake’s security boundary to expand cost-performance options.*
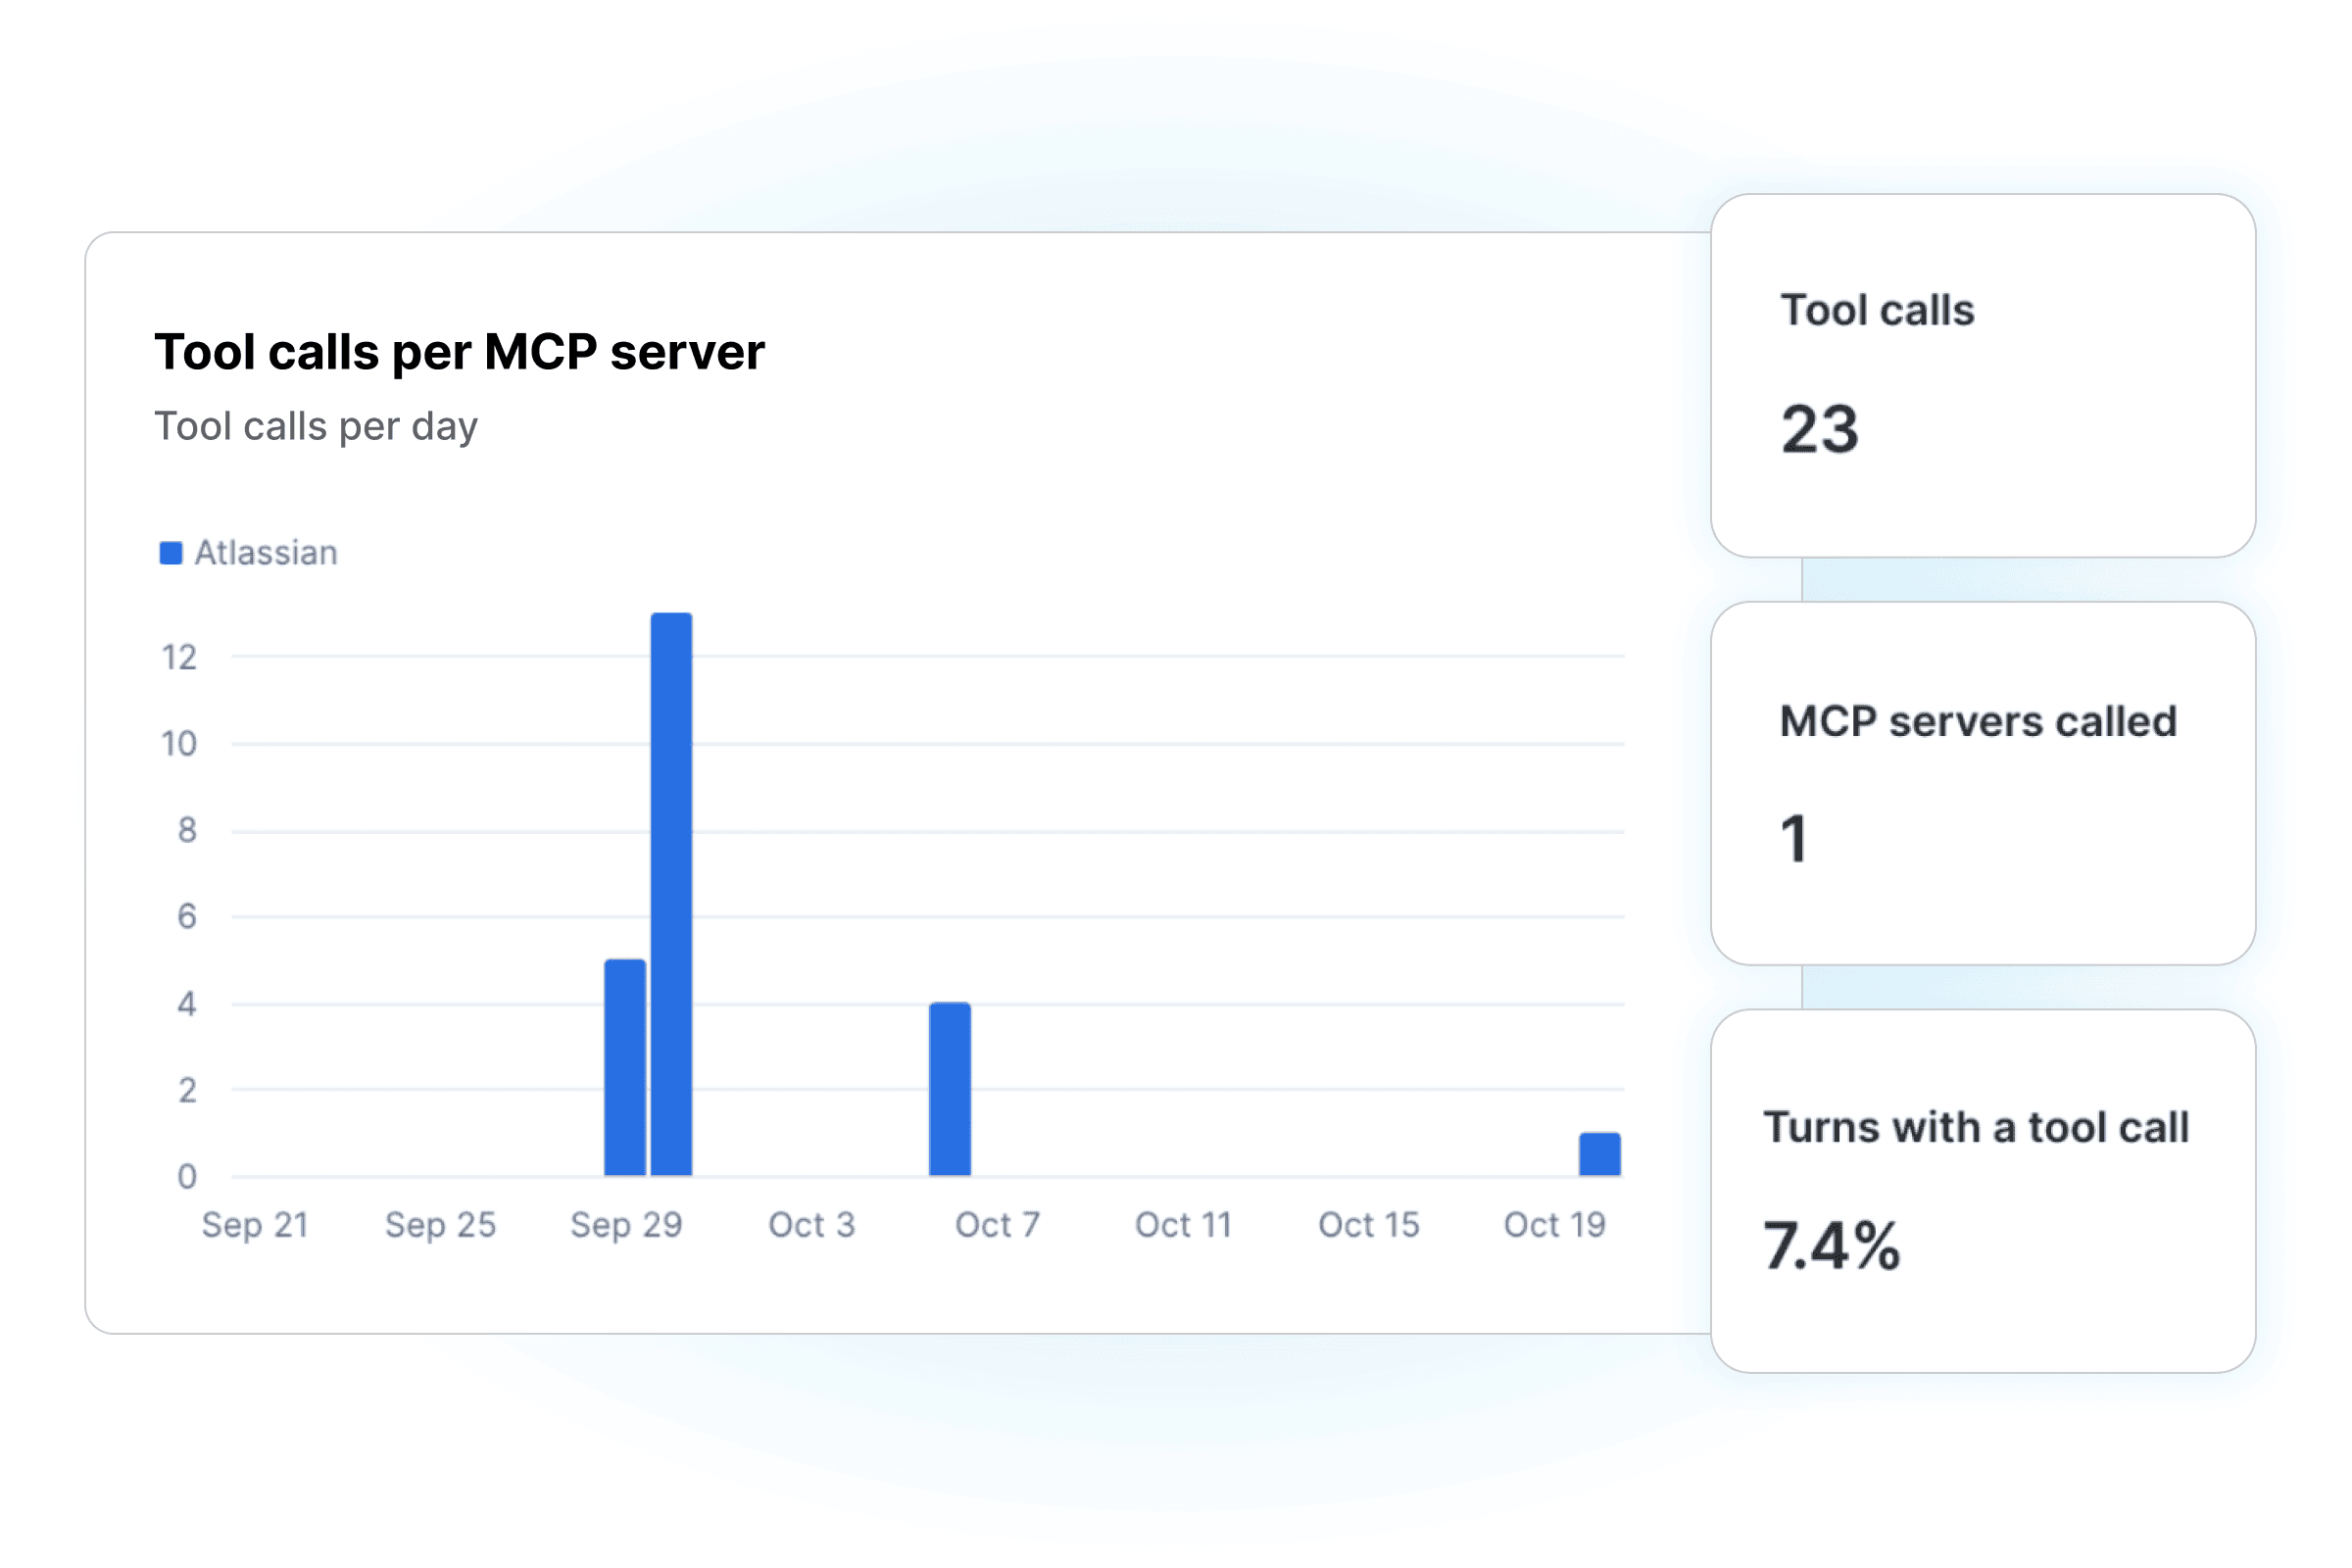
Manage actionable analytics
Catch failing tools and looping agents with Agent Trace Intelligence*
Cross-reference execution traces with business data to pinpoint costly agent loops, tools that aren’t working and the exact cost per completed task.
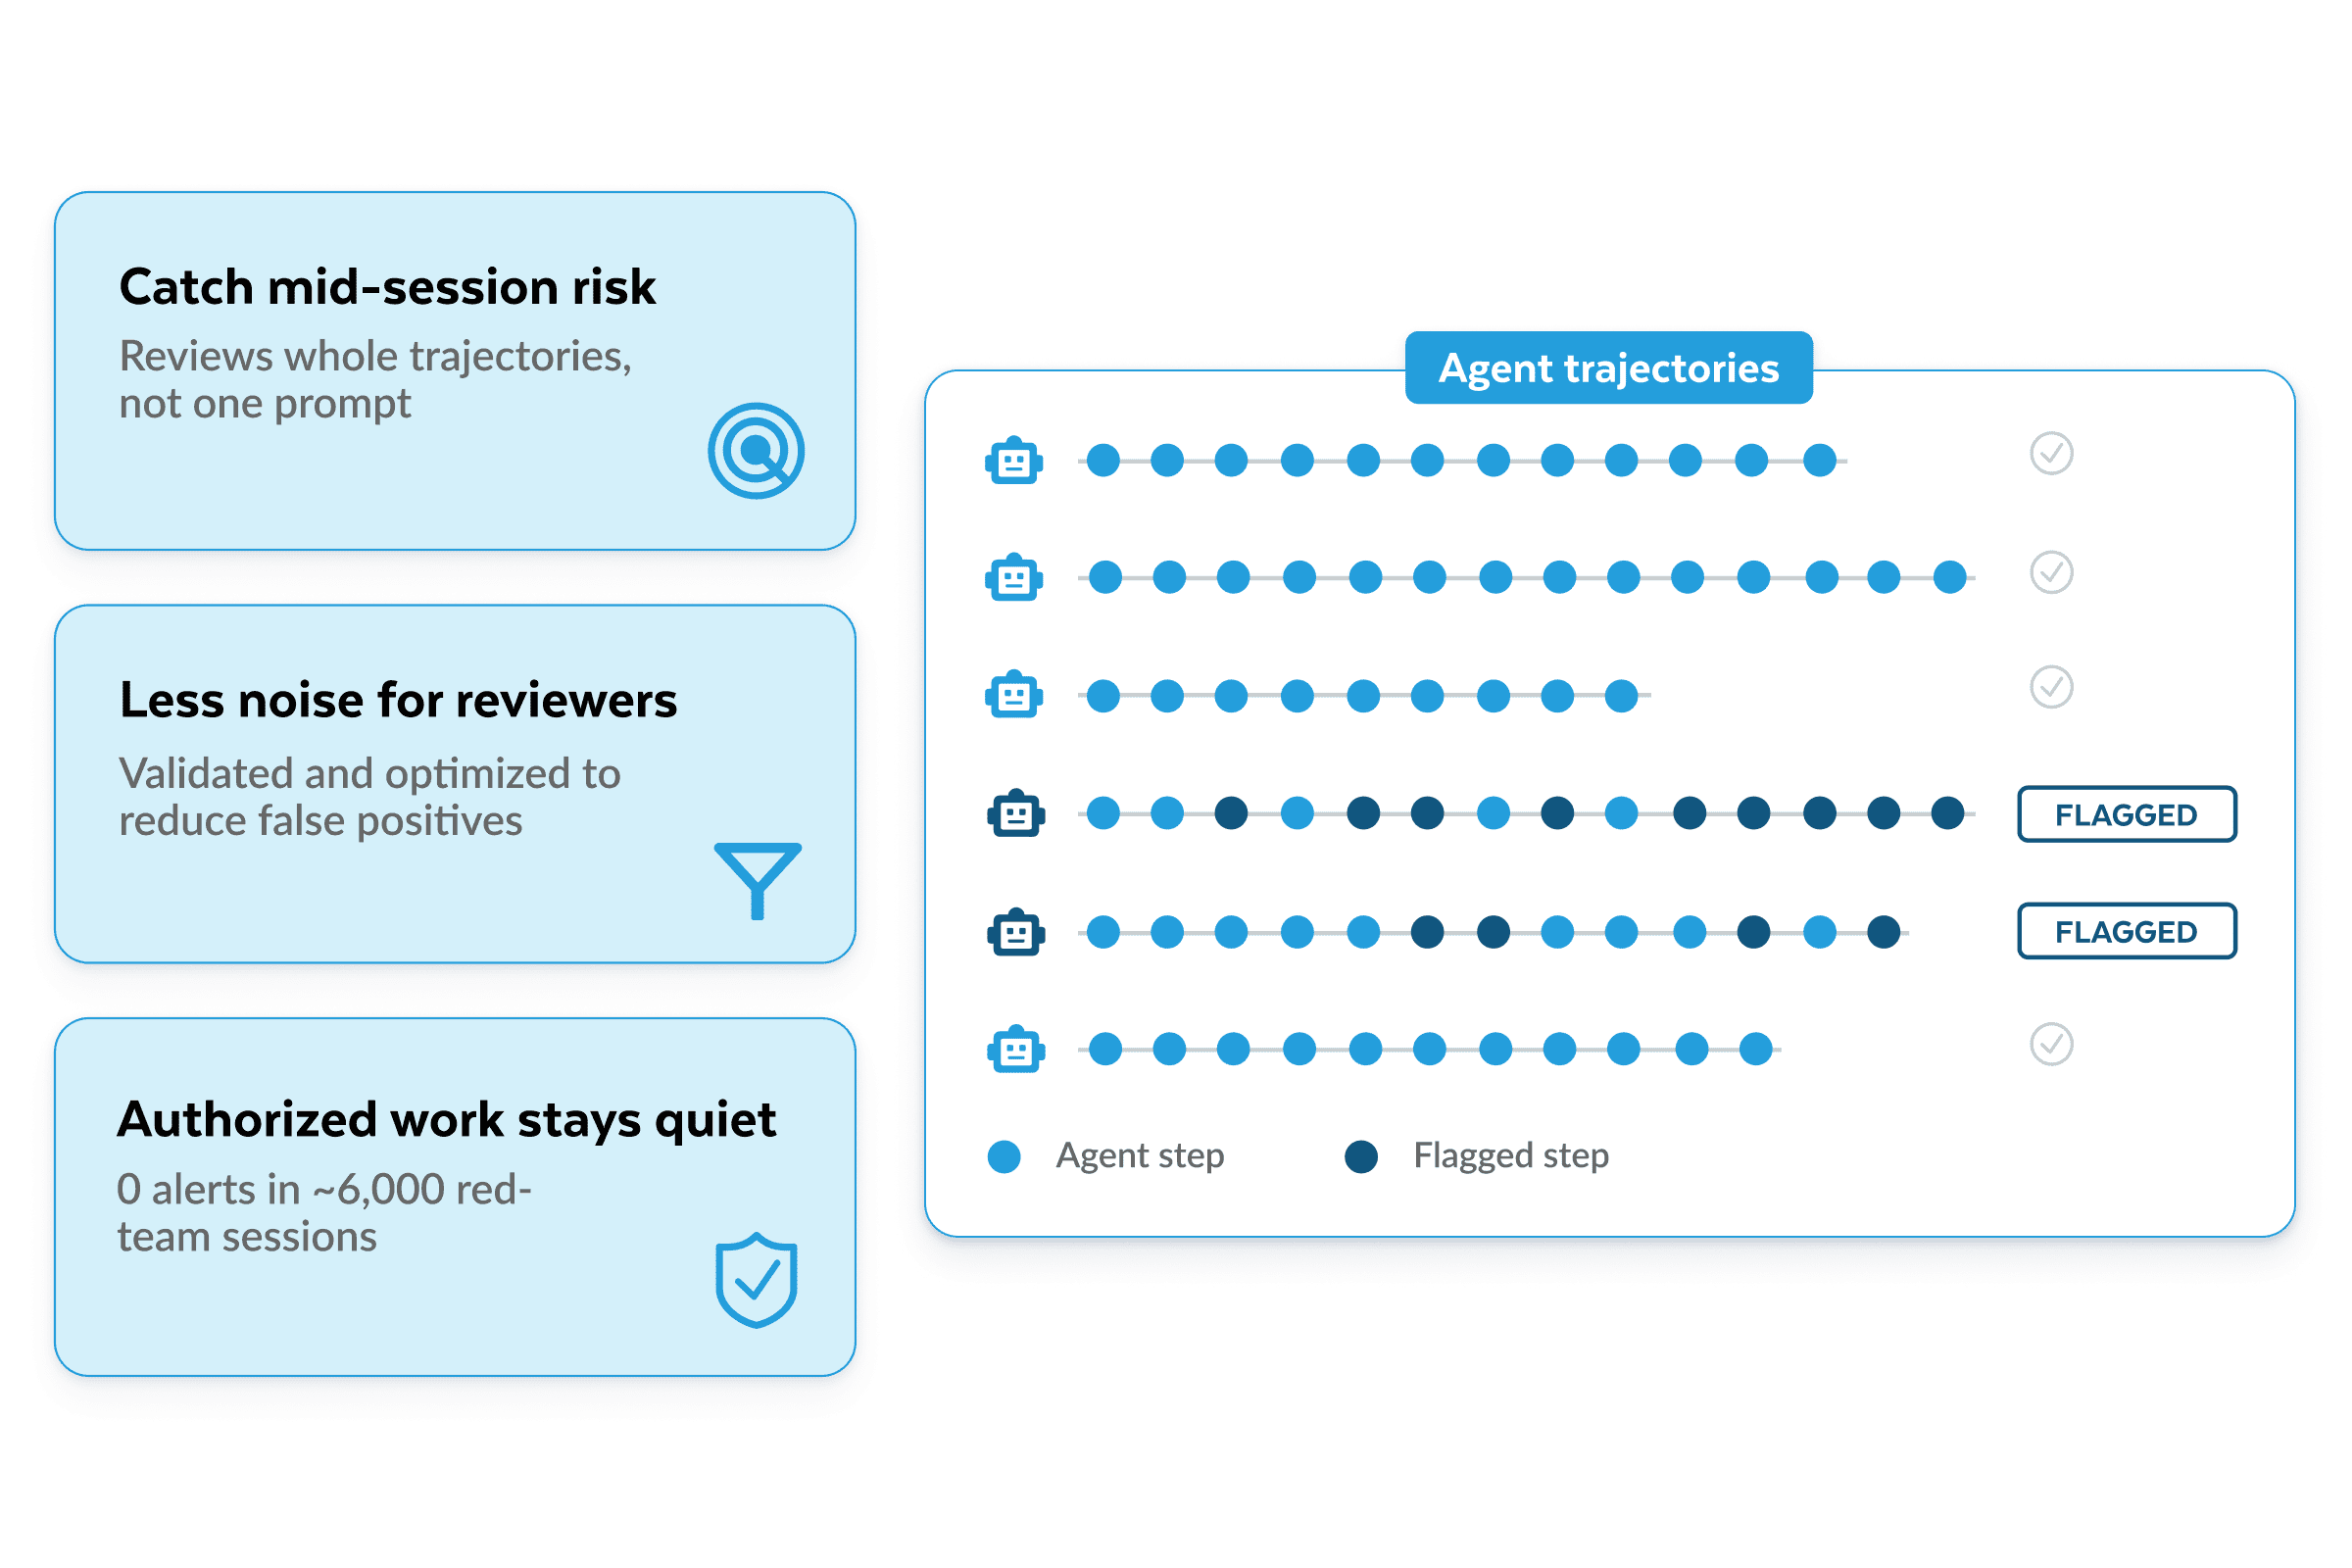
Dangerous Agent Activity Detection
Analyze multi-step agent activity to catch dangerous behavior*
- A two-stage engine pairs fast screening with context-aware reasoning, so security teams get clear findings backed by evidence instead of alert noise.
As a technical design partner on OpenAI Private Safety Processing (PSP), Snowflake built the engine to take in OpenAI's privacy-preserving safety signals, helping teams prioritize the highest-risk activity.
Cortex AI Gateway
Frequently Asked Questions
Answers to common questions about Cortex AI Gateway, AI agent governance, cost management and model routing.
Cortex AI Gateway is a secure, unified foundation that extends Snowflake's control plane to every AI agent — across any model, tool, framework and cloud. Unlike cloud providers that fragment agent governance across multiple surfaces, Cortex AI Gateway provides one experience to manage access, cost and compliance policies from a single foundation, regardless of which cloud your agents run on. Cortex AI Gateway governs from where the data lives — capturing every agent action in the customer's own Snowflake account and applying the policies already in place. No second identity framework, no new vendor required.
Cortex AI Gateway validates every MCP tool call before execution and applies the access policies your enterprise already has in Snowflake — no second identity framework required. This applies across 100+ MCP servers, including bring-your-own servers and VPC connections. Agents get access to approved tools without hardcoded credentials in agent code, so a compromised agent is designed not to exceed its current authorization. The Gateway logs every call in the customer's Snowflake account, where teams query it with standard SQL alongside their business data.
Cortex AI Gateway attributes AI spend to team, agent, department or app, so organizations know exactly where AI investment is going. Hard budget limits halt runaway agents before spend exceeds approved thresholds, with no manual intervention required. Dynamic model routing then matches each request to the right model for the task, reducing overspend on capability teams don't need.
Security and compliance teams get a single, auditable repository for each agent action — which tool was called, which system it touched, in what order and by whom — stored in the customer's own Snowflake account under existing governance policies. Shadow AI connections surface alongside sanctioned agents in the same view, so security teams see unsanctioned activity before incidents occur rather than after. Every record is queryable with standard SQL, with no exports, no new platform and no separate access request required.
