Feature
Snowflake operates as a global company, with its headquarters in the US, more than 10 affiliates in the EU and EEA, and close to 50 around the world. This overview outlines Snowflake’s sovereignty posture – focusing on current data residency controls and open standards that prevent vendor lock-in – alongside its strategic roadmap.
Snowflake is engaging with several EMEA sovereign cloud providers to offer both EU partner-operated sovereign deployments, and hybrid solutions that bring the capabilities of Snowflake to data stored on sovereign clouds in Europe.
Customers can choose their preferred deployment location(s) and configure their accounts so that customer data remains within the preferred region (e.g. the EU). Snowflake offers several EMEA regions across the three major cloud platforms (AWS, Azure, and GCP) giving customers flexibility to select the provider and location to meet their data residency requirements.
Snowflake's approach to foreign government access operates at two levels: legal process controls and customer-controlled technical notification measures.
Law Enforcement Requests Policy & Transparency Reports:
Snowflake maintains a publicly available Law Enforcement Requests Policy and publishes regular Transparency Reports covering US and non-US government requests.
Snowflake redirects government requestors to obtain customer data directly from the customer. When compelled to respond directly, Snowflake’s policy is to notify the affected customer unless legally prohibited; in which case it will use best efforts to request non-disclosure waivers, will document the request, and will notify the customer once legal restrictions are lifted. Snowflake carefully reviews the legality of each request, may challenge a request if we conclude there are reasonable grounds to consider it unlawful, and only discloses data under valid legal process.
Technical Notification Controls (customer-implemented):
Customers can safeguard sensitive columns using encryption keys hosted within their own KMS or HSM. Access to those columns at query time calls the customer's KMS creating an audit trail in systems the customer controls. Cross-referencing these key vault logs against Snowflake query history enables organizations to detect and document anomalous access.
Upon identifying a mismatch, customers can deploy two independent response options: selectively revoke specific column keys to isolate sensitive data while maintaining account operations, or revoke the account-level key via Tri-Secret Secure to trigger an immediate, platform-wide kill switch.
Snowflake supports customers in meeting their obligations under applicable EU legal and regulatory frameworks, including GDPR, DORA, NIS2, the EU Data Act, and the EU AI Act, among others, through a combination of technical controls, contract terms, and dedicated compliance documentation.
Snowflake customers located in the EU contract with a local EU-based affiliate, Snowflake Computing Netherlands B.V. (and not with Snowflake Inc. in the US). You can find the Snowflake Terms of Service here, EU-specific terms here (§ 3, European Economic Area), and more details on the contracting entities here.
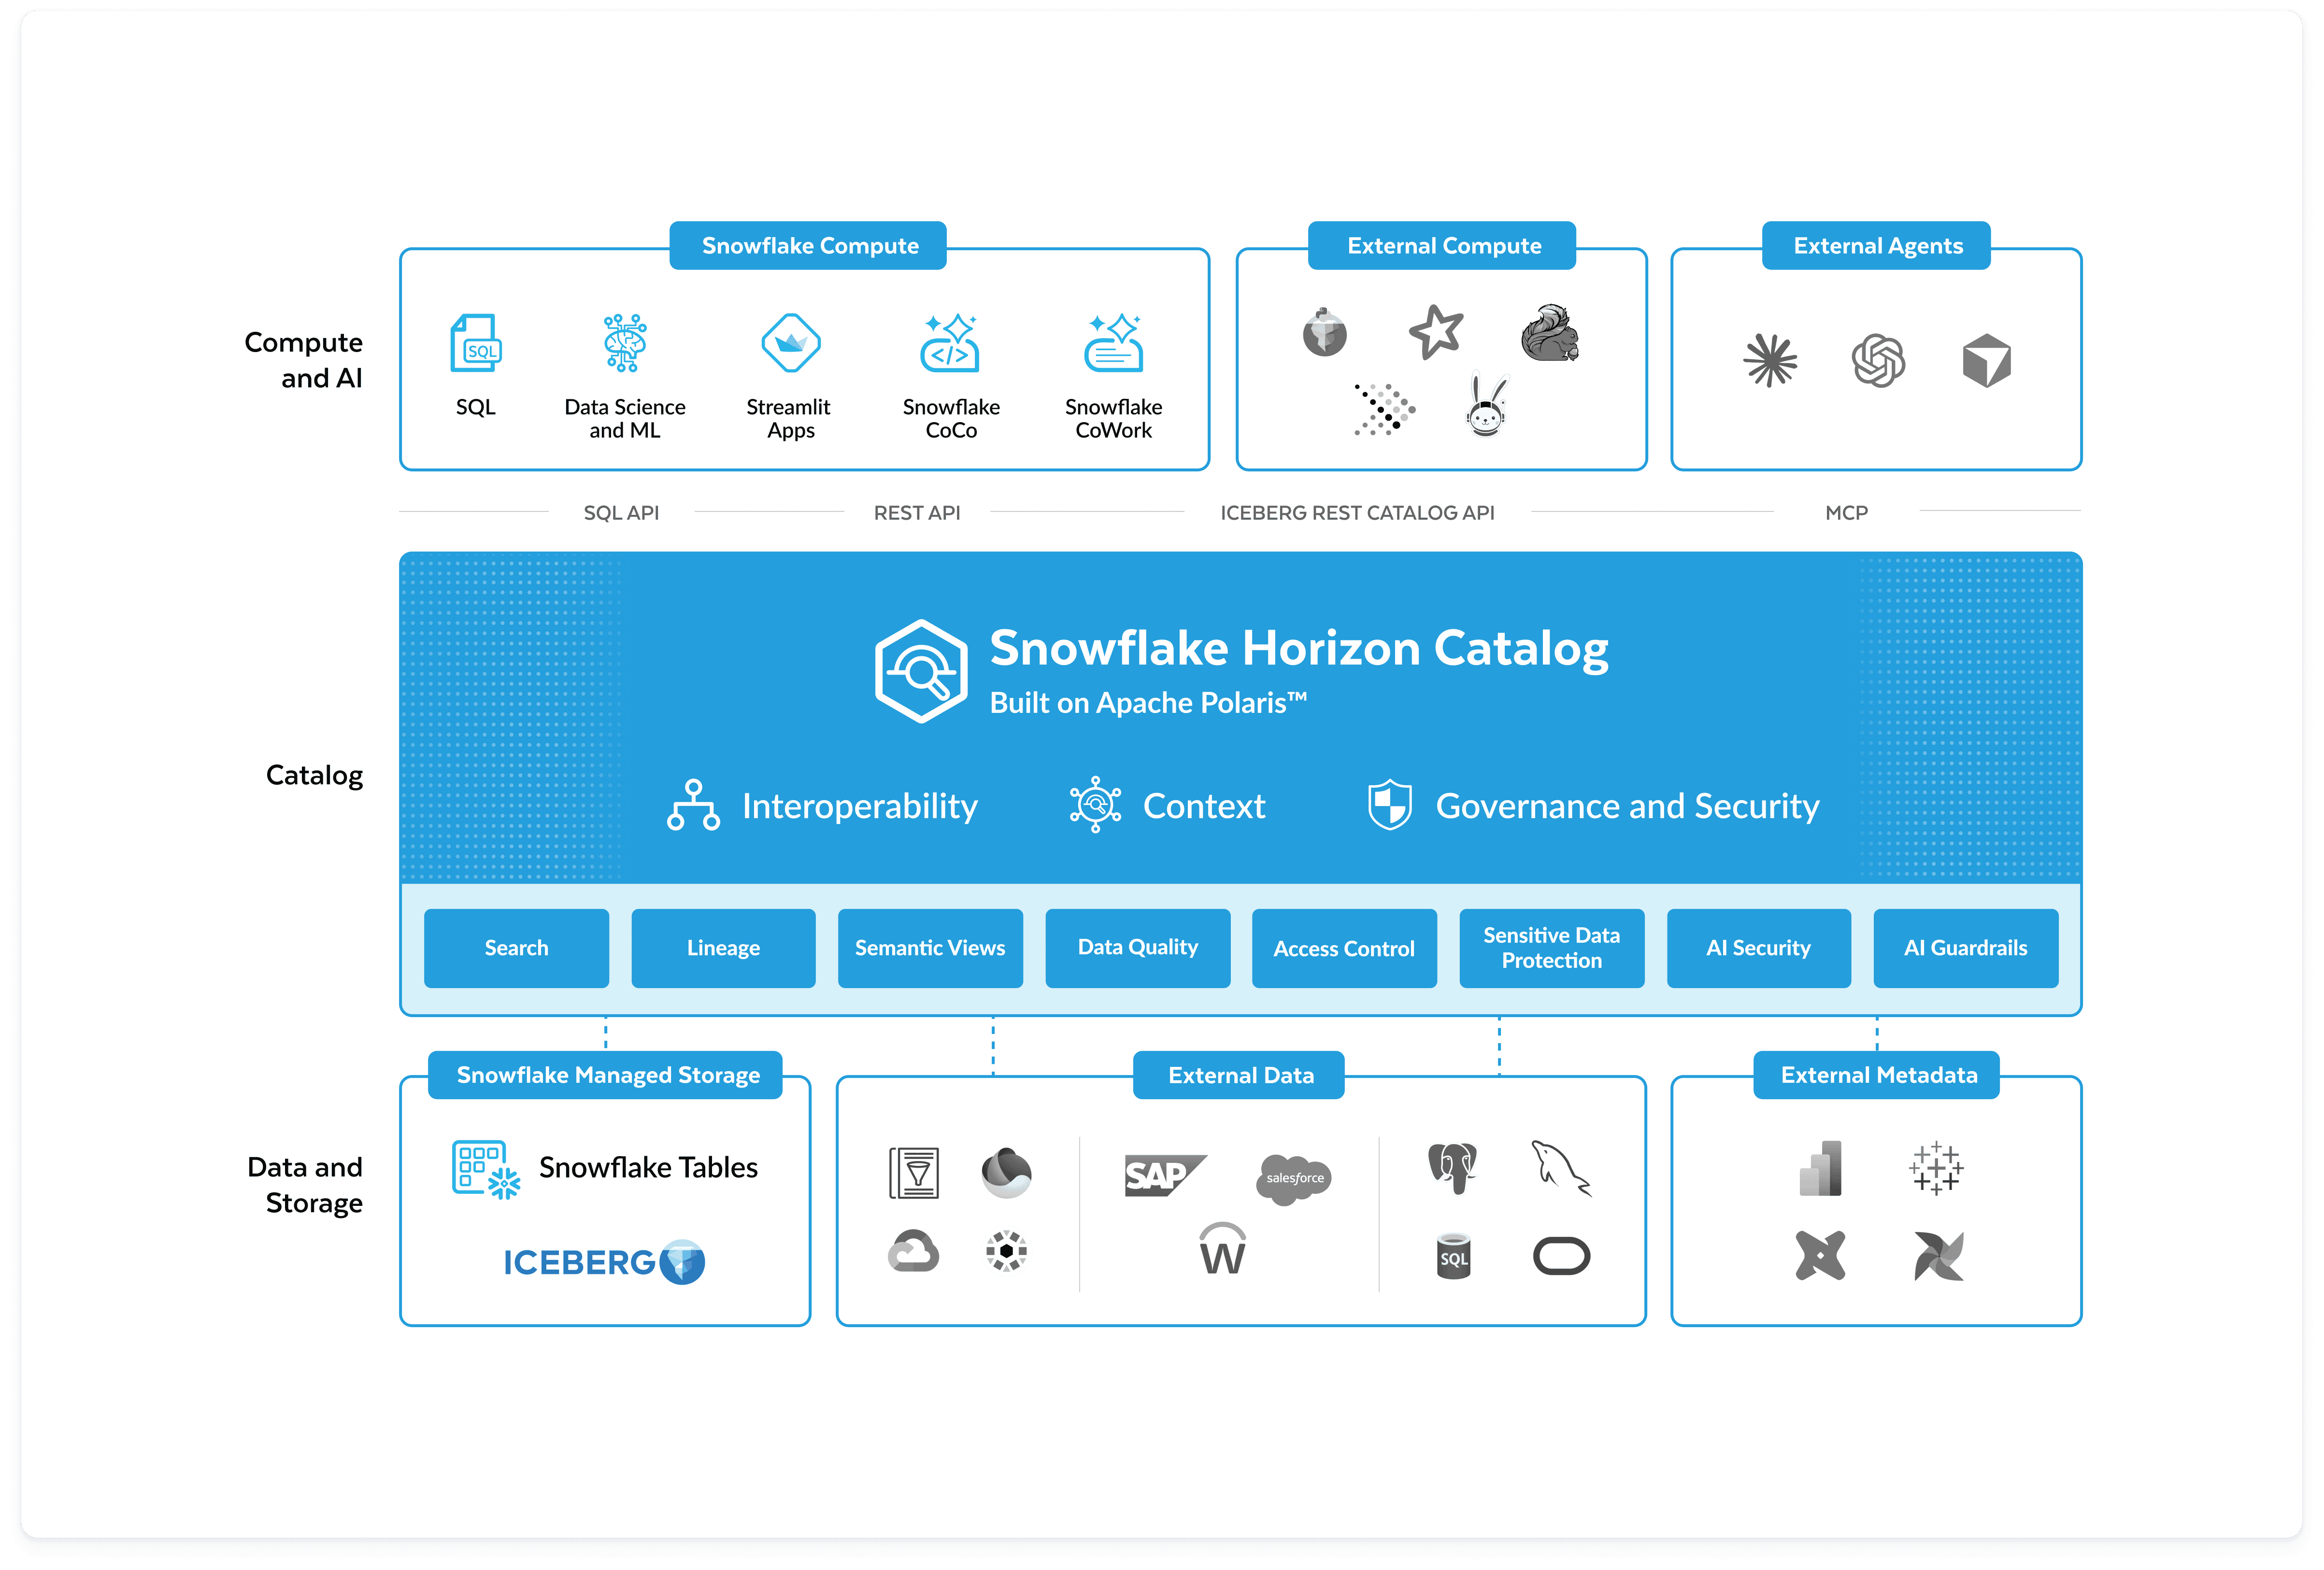
A distinctive characteristic of Snowflake's architecture is that customers can use Apache Iceberg's open table format, with the option to store data in their own external cloud storage — including S3-compatible storage hosted by sovereign cloud providers of their choice, using externally managed Iceberg tables. Because data is stored in the open Iceberg format, it can be read by any compatible engine (Apache Spark, Trino, and others) independently of Snowflake, directly supporting compliance with regulatory that have data portability requirements, such as EU Data Act.
This architectural approach separating compute from customer-owned storage gives customers direct, durable control over their data that persists independently of the provider relationship.
Snowflake is advancing its EU sovereignty strategy through strategic collaborations with EMEA sovereign cloud providers and regional operating partners. Designed to accommodate varying levels of sovereignty assurance, this roadmap focuses on two flexible deployment architectures:
EU Partner-Operated Deployments: Day-to-day operations, engineering, and support are managed entirely by an EU-based partner under a direct customer contract, limiting non-EU access. This model targets SEAL 2 (Proactive Sovereignty) in the near term with data residency, jurisdictional clarity, and operational control, with long-term alignment toward SEAL 3 (Digital Resilience).
Hybrid Sovereign Cloud Solutions: Brings Snowflake’s AI Data Cloud directly to data hosted within certified EMEA sovereign clouds. Customer data remains in open formats and is secured using sovereign-managed encryption keys.
Access Transparency: Snowflake provides customers with queryable audit logs of Snowflake operator access to their environments, giving customers visibility into, and the ability to evidence, any such access events. Additionally, Snowflake’s internal back-end access protocols are designed to avoid access to customer data except where necessary to fulfill a specific, documented request, such as a customer support engagement. Internal access requires a business justification and is logged.
By giving organizations the flexibility to select the deployment model, region, and infrastructure that best fit their regulatory and operational requirements, Snowflake promotes maximum customer optionality without sacrificing capability.
To learn more about Snowflake’s sovereign capabilities please work with your local sales team or get in touch with us.
This article contains forward-looking statements, including statements regarding planned partnerships, future product availability, deployment timelines, and roadmap direction, which are subject to risks and uncertainties and do not represent commitments to deliver specific features or timelines. Snowflake’s sovereign cloud partnerships and associated product capabilities are subject to ongoing development, partner agreements, and regulatory processes. Actual results and offerings may differ materially.


